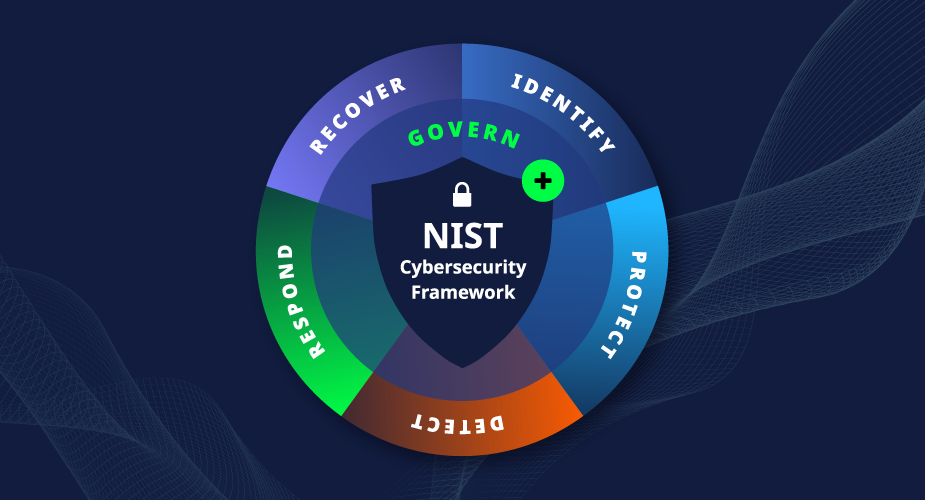
NIST Cybersecurity Framework for Small Business (Simplified)

What the NIST Cybersecurity Framework Is and Why Small Businesses Should Know It The NIST Cybersecurity Framework (CSF) is a voluntary set of guidelines developed by the US National Institute of Standards and Technology to help organisations of all sizes manage cybersecurity risk. First published in 2014, version 2.0 was released in February 2024 — … Read more

How to Prepare for a Cyber Insurance Audit: Small Business Checklist

The Shift That Changed Everything: From Questionnaire to Evidence Three years ago, a cyber insurance application was a questionnaire. You checked boxes: yes, we have antivirus; yes, we have a backup; yes, we have a firewall. Nobody verified. Premiums were low because underwriters were competing for market share. Then ransomware claims exploded. Insurers started paying … Read more

Cybersecurity Audit Checklist for Small Business (Free Template)

What a Cybersecurity Audit Actually Is (and Isn’t) A cybersecurity audit is a structured review of your business’s security controls against a defined standard — identifying what’s in place, what’s missing, and what needs improvement. For a small business, it doesn’t require an external auditor, a specialist tool, or a week of downtime. It requires … Read more

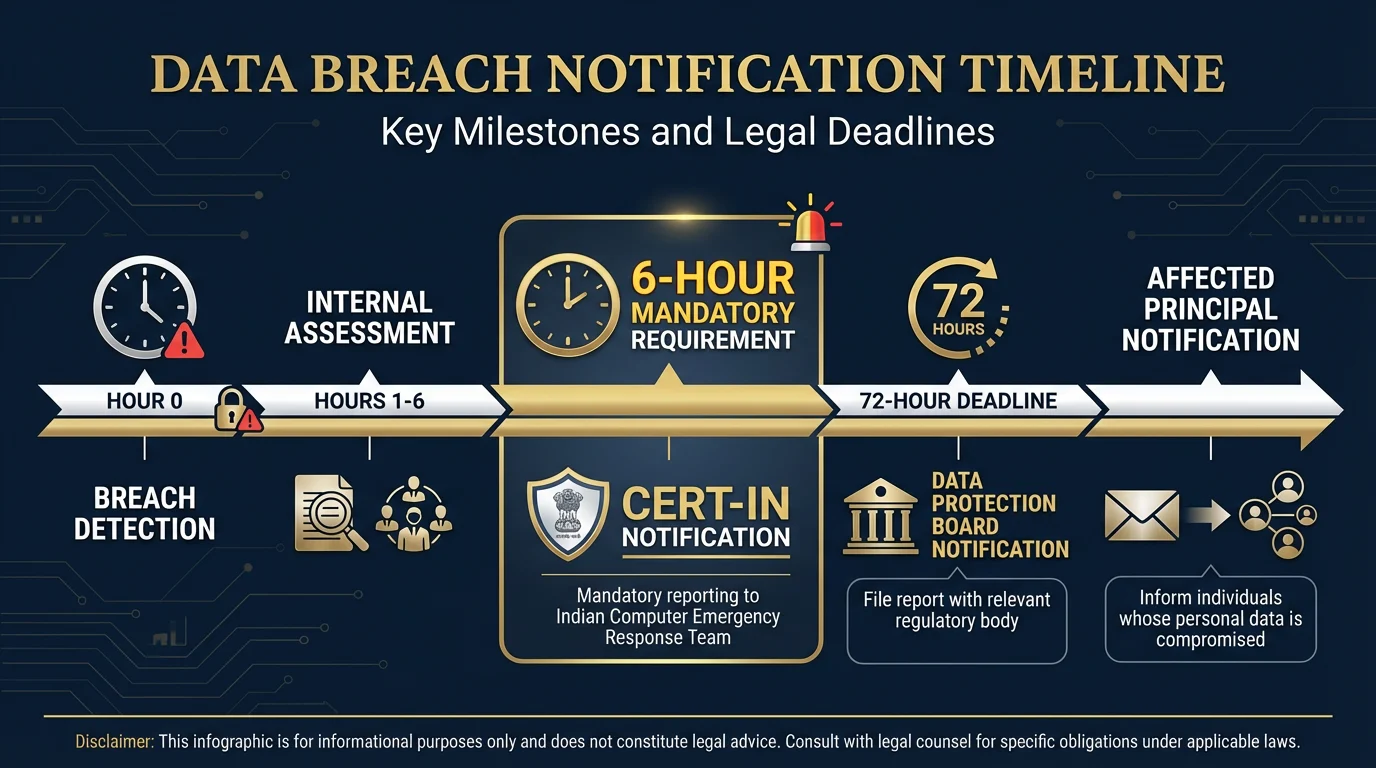
Data Breach Notification Requirements by Country (Small Business Guide)

This article provides general educational information. Data breach notification requirements are complex, jurisdiction-specific, and subject to change. Businesses facing an active breach should consult a qualified privacy attorney immediately. The Problem: When a Breach Happens, You Have Hours — Not Days — to Figure This Out A data breach is the worst week of most … Read more

GDPR vs CCPA: Key Differences for International Small Businesses

This article provides general educational information about GDPR and CCPA requirements. It is not legal advice. Businesses with specific compliance questions should consult a qualified privacy attorney. Why This Comparison Matters in 2026 Two years ago, the GDPR vs CCPA comparison was primarily an academic exercise for small businesses — most either had EU customers … Read more

PCI DSS Compliance for Small Business: Simple Checklist

This article provides general educational information about PCI DSS requirements. It is not legal or compliance advice. Businesses with specific compliance questions should consult a Qualified Security Assessor (QSA). What PCI DSS Is and Whether It Applies to You If your business accepts credit or debit card payments — in person, online, or by phone … Read more

EU NIS2 Directive: What Small Businesses Need to Know in 2026

This article provides general educational information about NIS2 requirements. It is not legal advice. Businesses with specific compliance questions should consult a qualified legal adviser in the relevant EU member state. The Most Important Question: Does NIS2 Apply to Your Business? The EU NIS2 Directive (Directive 2022/2555 on the Security of Network and Information Systems) … Read more

HIPAA Cybersecurity Requirements for Small Healthcare Businesses

This article provides general educational information about HIPAA requirements. It is not legal advice. Healthcare businesses with specific compliance questions should consult a qualified healthcare attorney or HIPAA compliance professional. The Most Important Thing to Know Before Reading This Article HHS published a proposed update to the HIPAA Security Rule in January 2025 — the … Read more

ISO 27001 vs SOC 2 for Small Businesses: Which Certification Do You Need?

This article provides general educational information. It is not legal or compliance advice. Businesses pursuing either certification should engage qualified compliance professionals and accredited auditors. The One Question That Decides This Before any comparison of frameworks, controls, timelines, or costs: who is asking? ISO 27001 and SOC 2 are not interchangeable. They are different artefacts … Read more